Workshop Short Description Templates
- Details
- By Mindy Schlueter
- Category: Workshop Short Description Templates
- Hits: 159
Cisco's AI Defense Workshop covers how to use the Cisco 3-step framework—Discovery, Detection, and Protection—to secure the AI lifecycle. Participants will practice running algorithmic red teaming simulations, scanning model files for malicious payloads, and configuring runtime guardrails. The workshop also covers securing agentic workflows using the Model Context Protocol (MCP) to prevent goal hijacking and context poisoning.
What to expect
You will work through the workshop as a Senior Security Engineer at PseudoCo, a fictional organization deploying generative and agentic AI across its enterprise. The workshop covers four use cases and fifteen success criteria.
The workshop includes:
- AI asset discovery using Cisco AI Defense
- Algorithmic red teaming to test models for prompt injection, jailbreaking, and harmful content generation
- Model file scanning for embedded threats in
.pkl,.h5, and.onnxfiles - Runtime policy configuration to block PII, PHI, and PCI data leaks
- MCP server scanning for vulnerabilities and intent-based threats
- Agentic protection against tool poisoning, prompt injection, and rug pull attacks
- Side-by-side testing of Monitor and Enforce policy modes using the AI Defense Demo Runner
Who should attend
- Security engineers and architects
- AI and ML platform owners
- Application security teams
- IT and security leaders responsible for AI governance
What you will learn
- How Cisco AI Defense applies the Discovery, Detection, and Protection framework to AI systems
- How to validate models before deployment and protect them at runtime
- How to detect and block agentic AI threats specific to MCP-based architectures
- How to build runtime policies that enforce data protection and content safety
- Details
- By Matt Okuma
- Category: Workshop Short Description Templates
- Hits: 387
Course Title: One Cisco Experience Lab
Direct Workshop Link: https://ciscosecurityworkshop.com/workshops/mod/page/view.php?id=8229
Course Description:
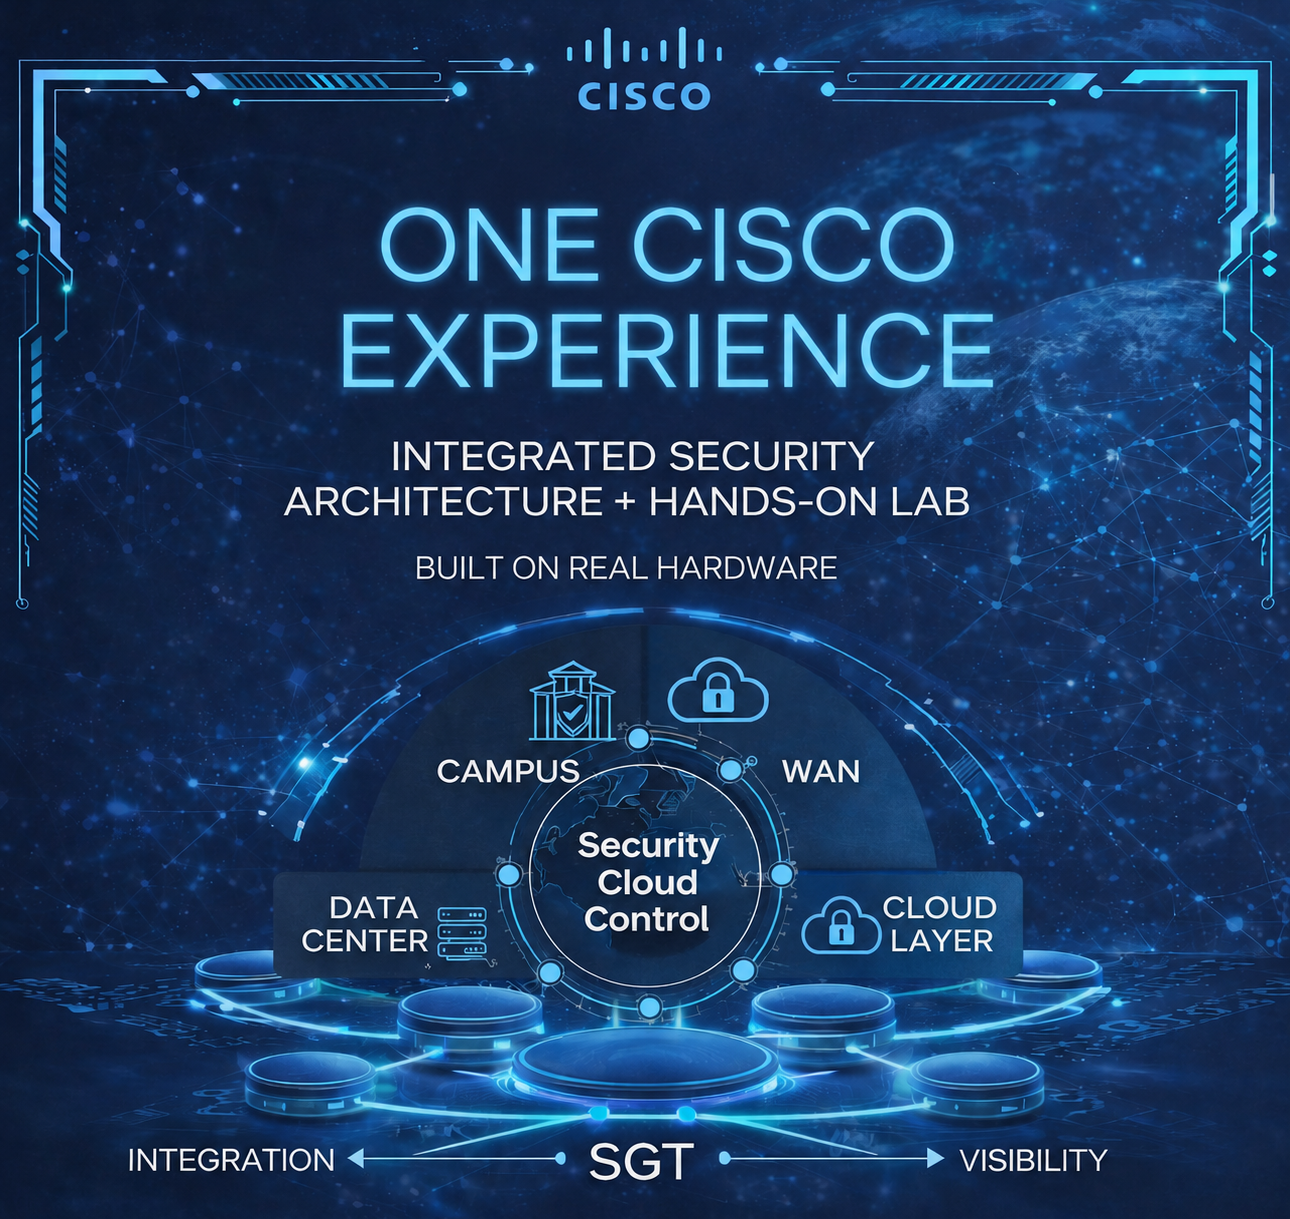
Get hands-on with the One Cisco Experience by unifying networking, security, observability, and policy into a single integrated architecture designed to protect modern enterprises across campus, branch, WAN, cloud, and remote access environments. By combining deep visibility, identity-driven access control, and Zero Trust enforcement across every connection point, organizations can simplify operations, strengthen security posture, and improve digital resilience.
In this hands-on lab, participants will deploy either a BGP EVPN fabric or an SDA-LISP Campus fabric as the foundation for a modern Cisco Network supporting both macro and micro segmentation. Through guided exercises, you’ll experience how Cisco technologies work together seamlessly across domains using Cisco Security Cloud Control, Secure Firewall Management Center (cdFMC/FTD), Cisco Secure Access, Duo, Catalyst SD-WAN, Identity Services Engine (ISE), ThousandEyes, and Security Group Tags (SGTs) to deliver unified policy enforcement, shared telemetry, and consistent user experiences.
You’ll implement integrated workflows that connect networking and security operations across campus, branch, data center, and remote users. Real-world use cases include securing users and devices accessing local and cloud applications, protecting IoT environments through identity-based segmentation, and enabling secure remote access using Zero Trust Access (ZTA). Participants will also explore how Cisco’s unified platform approach enables consistent policy, end-to-end visibility, and faster troubleshooting across switching, wireless, SD-WAN, cloud security, and firewall infrastructure.
By the end of the lab, you’ll gain practical experience deploying and validating a fully integrated Cisco architecture that demonstrates the power of the One Cisco Experience—bringing together connectivity, security, and observability into a cohesive operational model for the modern enterprise.
Workshop Highlights
- Build a Modern Cisco Network: Deploy either a Cisco SDA-LISP Campus Fabric or BGP EVPN Fabric as the foundation for Zero Trust segmentation and secure connectivity.
- Hands-On Zero Trust Implementation: Configure identity-based access control, SGT-driven segmentation, Secure Access, Duo MFA, and Secure Firewall policy enforcement across campus, WAN, and remote access environments.
- End-to-End Security Integration: Integrate Cisco Security Cloud Control, ISE, Secure Access, SD-WAN, ThousandEyes, and Secure Firewall for unified policy and telemetry sharing.
- Real-World Security Use Cases: Secure users, IoT devices, branch connectivity, SaaS applications, and private applications using practical enterprise scenarios.
- Guided Expert-Led Labs: Follow step-by-step exercises with instructor and proctor support while validating policy enforcement, segmentation, and observability across the infrastructure.
Key Takeaways
- Practical experience deploying a Zero Trust-based Cisco Network architecture.
- Hands-on skills configuring macro and micro segmentation using Virtual Networks (VNs), TrustSec, and Security Group Tags (SGTs).
- Experience integrating Cisco ISE, Duo, Active Directory, Secure Access, SD-WAN, and Secure Firewall into a unified policy framework.
- Understanding of secure remote access technologies including ZTNA, VPN-as-a-Service, and browser-based access.
- Skills to deploy and validate secure campus and branch architectures using Cisco Catalyst Center, SDA, EVPN, and SD-WAN.
- Experience using ThousandEyes and telemetry tools for visibility, monitoring, and troubleshooting.
- Confidence troubleshooting identity, policy, segmentation, and connectivity issues across enterprise environments.
Who Should Attend
- Network engineers and architects designing modern enterprise campus, branch, and WAN infrastructures.
- Security engineers implementing Zero Trust, segmentation, and secure access solutions.
- IT professionals responsible for campus networking, SD-WAN, wireless, or data center security.
- Cisco partners, consultants, and technical teams supporting modern Networking deployments.
- Anyone interested in gaining hands-on experience with Cisco’s integrated Zero Trust and modern Networking architecture.
Workshop Format
- Hands-On Lab: Interactive guided exercises in a fully integrated Hardware Based lab environment.
- Real-World Enterprise Scenarios: Deploy and validate policies across campus, WAN, remote access, IoT, and data center environments.
- Step-by-Step Guided Labs: Instructor-led walkthroughs with hands-on implementation and validation tasks.
- Dedicated Hardware POD Access: Access to a dedicated hardware pod lab environment for independent configuration and testing.
- Expert Support: Live assistance from experienced Cisco Proctors throughout the workshop.
Prerequisites
- Familiarity with basic networking concepts including routing, switching, and wireless networking.
- Basic understanding of security concepts such as VPNs, segmentation, identity, and access control.
- Prior exposure to Cisco networking or security technologies is helpful but not required.
- General knowledge of enterprise networking environments, SD-WAN, or campus architectures is recommended.
- Access to a Cisco dCloud account (provided as part of the course)
Why Attend?
This workshop provides a unique opportunity to gain practical, hands-on experience building and securing a modern enterprise network using Cisco’s Zero Trust architecture. Rather than only learning the concepts, you’ll deploy, integrate, validate, and troubleshoot real security and networking technologies across campus, branch, WAN, cloud, and remote access environments. By the end of the lab, you’ll have the knowledge and confidence to implement unified policy enforcement, secure segmentation, observability, and secure access strategies that help organizations reduce risk and strengthen digital resilience.
- Details
- By Jamie Cresdee
- Category: Workshop Short Description Templates
- Hits: 1490
The Hybrid Mesh Firewall: Project Meteor workshop is designed to equip participants with the knowledge and hands-on experience needed to modernize firewall strategies using Cisco’s Hybrid Mesh Firewall technology. This innovative solution unifies security across data centers, cloud, campus, and IoT environments, providing a highly distributed security fabric.
During this session, you will step into the shoes of a fictional engineer at PseudoCo and work through real-world scenarios that highlight the power and flexibility of Cisco’s security solutions.
The workshop will make extensive use of Cisco Security Cloud Control and cover topics such as deployment, SD-WAN configuration, shared objects management, and application segmentation. This is a great opportunity to build hands-on experience and deepen your understanding of modern network security practices through a self-paced workshop.
Key Takeaways
- Clear understanding of Cisco’s Hybrid Mesh Firewall solution and its advantages
- Gain hands-on experience with Cisco Security Cloud Control for centralized and extensive security management
- Understand how to configure SD-WAN for optimized and secure network connectivity
- Explore enhanced cloud visibility to monitor and protect distributed applications and data
- Deepen your knowledge of Shared Objects and their role in efficient policy management
- Master application segmentation techniques using both endpoint agents and the firewall for comprehensive security.
Who Should Attend
- Anyone involved in firewall management, policy enforcement, or security modernization initiatives
Workshop Format
- Duration: 2 hours
- Structure: A multi-phase, self-contained hands-on workshop
- Phases Include:
- Onboarding firewalls and simplifying branch connectivity
- Integrating cloud policies and multi-cloud defense
- Configuring segmentation for workloads and applications
- Testing threat detection capabilities including encrypted traffic inspection
- Tools Used: Cisco Security Cloud Control, Secure Firewall, Multi-cloud Defense and Secure Workload
Prerequisites
- Cisco account registration (CCOID) – Click here for more information
- Cisco Security Workshop account registration – Click here to register
- Basic understanding of firewall concepts and network security
Why Attend This Workshop
In today’s complex and rapidly evolving threat landscape, traditional firewall approaches are no longer sufficient. The Hybrid Mesh Firewall: Project Meteor workshop empowers you to modernize your security posture by adopting a distributed firewall fabric that scales with your enterprise needs. Attendees will gain practical skills to reduce attack surfaces, prevent lateral movement, and protect critical applications across hybrid environments. This workshop offers a unique opportunity to experience Cisco’s cutting-edge firewall technology firsthand, enabling you to lead your organization’s security transformation with confidence and agility.
- Details
- By Brandon Newport
- Category: Workshop Short Description Templates
- Hits: 846
Experience the latest innovations in Cisco Secure Firewall 10.0 in this lab. Discover how the Encrypted Visibility Engine (EVE) enables threat detection in encrypted traffic, while AI-driven SnortML provides protection against signature-less attacks. Take advantage of expanded SD-WAN features and improved OT security with advanced access control and containment. Seamless Splunk integration delivers robust security analytics for effective incident response. This lab will help you build the knowledge and skills needed to highlight the strengths of Cisco Secure Firewall 10.0.
Page 1 of 5