Search results
AI Defense Workshop - Sept. 16th
Cisco's AI Defense Workshop covers how to use the Cisco 3-step framework—Discovery, Detection, and Protection—to secure the AI lifecycle. Participants will practice running algorithmic red teaming simulations, scanning model files for malicious payloads, and configuring runtime guardrails. The workshop also covers securing agentic workflows using the Model Context Protocol (MCP) to prevent goal hijacking and context poisoning.
What to expect
You will work through the workshop as a Senior Security Engineer at PseudoCo, a fictional organization deploying generative and agentic AI across its enterprise. The workshop covers four use cases and fifteen success criteria.
The workshop includes:
- AI asset discovery using Cisco AI Defense
- Algorithmic red teaming to test models for prompt injection, jailbreaking, and harmful content generation
- Model file scanning for embedded threats in
.pkl,.h5, and.onnxfiles - Runtime policy configuration to block PII, PHI, and PCI data leaks
- MCP server scanning for vulnerabilities and intent-based threats
- Agentic protection against tool poisoning, prompt injection, and rug pull attacks
- Side-by-side testing of Monitor and Enforce policy modes using the AI Defense Demo Runner
Who should attend
- Security engineers and architects
- AI and ML platform owners
- Application security teams
- IT and security leaders responsible for AI governance
What you will learn
- How Cisco AI Defense applies the Discovery, Detection, and Protection framework to AI systems
- How to validate models before deployment and protect them at runtime
- How to detect and block agentic AI threats specific to MCP-based architectures
- How to build runtime policies that enforce data protection and content safety
| Event Date | 2026-09-16 |
| Event Location Timezone | America/New_York |
| Event Start Time | 10:50 AM |
| Event End Time | 11:00 PM |
| Capacity | 75 |
| Registered | 4 |
| Available Place | 71 |
| Created By | Brandon Anastasoff |
| Location | Virtual |
Cisco SASE Experience Lab Thursday 17-Sep-26
Cisco SASE Experience Lab
Today’s enterprise IT, networking, and security professionals require solutions that are straightforward, simple, and effective. At Cisco, we eliminate complexity to deliver a seamlessly integrated experience for both users and IT teams.
The Cisco Secure Access Service Edge (SASE) Experience Workshop is a facilitator-led, practical training designed to provide participants with immersive, hands-on experience using Cisco Catalyst SD-WAN and Cisco Secure Access (SSE) solutions. During the workshop, attendees engage in realistic lab exercises within a fully provisioned cloud environment, experiencing both end-user and administrator perspectives.
This workshop combines networking, security, and observability to enable seamless, secure access to applications wherever users work. It supports zero trust principles and cloud-native deployment models, empowering you with the tools and knowledge to optimize your security posture and connectivity performance.
This session is designed to equip you with the expertise needed to confidently understand and operate a scalable, high-performance Cisco SASE architecture that meets today’s dynamic enterprise demands.
| Event Date | 2026-09-17 |
| Event Location Timezone | America/New_York |
| Event Start Time | 9:00 AM |
| Event End Time | 11:55 PM |
| Capacity | 50 |
| Registered | 12 |
| Available Place | 38 |
| Created By | Steve Marcinek |
| Location | Virtual |
Mock AI Defense Workshop for NYC SEs
This is the AI Defense Mock Workshop
| Event Date | 2026-09-19 |
| Event Location Timezone | America/New_York |
| Event Start Time | 6:00 PM |
| Event End Time | 9:00 PM |
| Capacity | 20 |
| Registered | 1 |
| Available Place | 19 |
| Created By | Derwin Warren |
| Location | Virtual |
BT Firewall Training Session 2
The Hybrid Mesh Firewall: Project Meteor workshop is designed to equip participants with the knowledge and hands-on experience needed to modernize firewall strategies using Cisco’s Hybrid Mesh Firewall technology. This innovative solution unifies security across data centers, cloud, campus, and IoT environments, providing a highly distributed security fabric.
During this session, you will step into the shoes of a fictional engineer at PseudoCo and work through real-world scenarios that highlight the power and flexibility of Cisco’s security solutions.
The workshop will make extensive use of Cisco Security Cloud Control and cover topics such as deployment, SD-WAN configuration, shared objects management, and application segmentation. This is a great opportunity to build hands-on experience and deepen your understanding of modern network security practices through a self-paced workshop.
Key Takeaways
- Clear understanding of Cisco’s Hybrid Mesh Firewall solution and its advantages
- Gain hands-on experience with Cisco Security Cloud Control for centralized and extensive security management
- Understand how to configure SD-WAN for optimized and secure network connectivity
- Explore enhanced cloud visibility to monitor and protect distributed applications and data
- Deepen your knowledge of Shared Objects and their role in efficient policy management
- Master application segmentation techniques using both endpoint agents and the firewall for comprehensive security.
Who Should Attend
- Anyone involved in firewall management, policy enforcement, or security modernization initiatives
Workshop Format
- Duration: 2 hours
- Structure: A multi-phase, self-contained hands-on workshop
- Phases Include:
- Onboarding firewalls and simplifying branch connectivity
- Integrating cloud policies and multi-cloud defense
- Configuring segmentation for workloads and applications
- Testing threat detection capabilities including encrypted traffic inspection
- Tools Used: Cisco Security Cloud Control, Secure Firewall, Multi-cloud Defense and Secure Workload
SHAPE
Prerequisites
- Cisco account registration (CCOID) – Click here for more information
- Cisco Security Workshop account registration – Click here to register
- Basic understanding of firewall concepts and network security
SHAPE
Why Attend This Workshop
In today’s complex and rapidly evolving threat landscape, traditional firewall approaches are no longer sufficient. The Hybrid Mesh Firewall: Project Meteor workshop empowers you to modernize your security posture by adopting a distributed firewall fabric that scales with your enterprise needs. Attendees will gain practical skills to reduce attack surfaces, prevent lateral movement, and protect critical applications across hybrid environments. This workshop offers a unique opportunity to experience Cisco’s cutting-edge firewall technology firsthand, enabling you to lead your organization’s security transformation with confidence and agility.
| Event Date | 2026-09-21 |
| Event Location Timezone | UTC |
| Event Start Time | 9:00 AM |
| Event End Time | 12:00 PM |
| Capacity | 20 |
| Registered | 0 |
| Available Place | 20 |
| Created By | Bhupinder Singh |
| Location | Virtual |
Purple Teaming with Cisco & Region Syddanmark
This instructor led lab will walk attendees through a purple teaming exercise with Cisco XDR. Each attendee will be assigned a pod with test machines and Cisco Security tools predeployed. Starting with red team activities attendees will gain initial access to a victim machine using a phishing email and the proceed to launch payloads using a variety of MITRE TTP's. After running an attack attendees will start blue team activities to review the detections in Secure Endpoint, Secure Firewall, and Cisco XDR. Blue team activities entail sifting through device trajectory and investigating incidents using the XDR toolset.
Attendees will experience running an attack and using Cisco Security tools to remediate the threats gaining hands on purple teaming experience.
Training Outline:
Introduction (15 mins)
Blind Eagle Attack Emulation (1 hour)
Blue Teaming for Blind Eagle Attack (1 hour)
Closing and Q&A (15 mins)
| Event Date | 2026-09-21 |
| Event Location Timezone | Europe/Copenhagen |
| Event Start Time | 1:00 PM |
| Event End Time | 4:00 PM |
| Capacity | 10 |
| Registered | 0 |
| Available Place | 10 |
| Created By | Lars Siegumfeldt |
| Location | Virtual_DK |
Pacific Source Secure Access Workshop
Lab guide access for workshop
| Event Date | 2026-09-21 |
| Event Location Timezone | America/Los_Angeles |
| Event Start Time | 8:30 AM |
| Event End Time | 8:00 PM |
| Capacity | 5 |
| Registered | 1 |
| Available Place | 4 |
| Created By | Gosha Maruzhenko |
| Location | Virtual |
Monoprice Secure Internet Access Lab
Course Title:
Designing and Deploying Zero Trust Access with Duo Identity and Cisco Secure Access
Course Description:
Step into the role of a network security administrator in this guided, hands-on workshop. You’ll learn how to design, deploy, and validate a modern Zero Trust Access solution using Duo Directory and Cisco Secure Access. Acting as the administrator for the fictional organization PseudoCo, you will configure secure connectivity between remote users and private applications hosted in a secure data center.
You’ll have full administrative access to a dedicated virtual data center environment in Cisco’s dCloud, pre-provisioned with Duo and Secure Access services. Each participant receives a unique Duo tenant and Secure Access organization, enabling you to configure and test infrastructure in any Duo region or Secure Access region, with recommendations to align settings with your specific dCloud Data Center location.
Workshop Highlights
- Real-World Zero Trust Scenarios: Configure secure connectivity for remote users, private applications, and secure Internet access
- Hands-On Labs: Access to a fully provisioned virtual data center and unique Secure Access organization.
- End-to-End Deployment: Learn to set up secure Identity, VPNs, IP pools, and tunnels for seamless, secure access.
- Expert Guidance: Step-by-step lab exercises and access to proctors for support.
Key Takeaways
- Practical experience deploying Zero Trust Access solutions using Duo Identity and Cisco Secure Access.
- Skills to configure and validate secure connections between distributed users and applications.
- Understanding of best practices for aligning Secure Access configurations with data center regions.
Who Should Attend
- IT and network administrators responsible for securing enterprise access.
- Security engineers and architects interested in Zero Trust methodologies.
- Anyone preparing to deploy Duo or Cisco Secure Access solutions in their organization.
Workshop Format
- Hands-On Labs: Interactive, guided exercises in a live dCloud virtual environment.
- Instructor Support: Direct assistance from proctors and subject matter experts.
- Individual Access: Each attendee receives their own Duo account and Secure Access organization and isolated lab environment.
Prerequisites
- Familiarity with basic networking and security concepts.
- Prior experience with remote access technologies or Cisco solutions is helpful but not required.
- Access to a Cisco dCloud account (provided as part of the course).
Why Attend?
This workshop offers a unique, practical opportunity to master Zero Trust Access with Duo Identity and Cisco Secure Access in a risk-free, fully supported lab environment. You’ll leave with the confidence and know-how to implement secure, modern access solutions tailored to your organization’s needs.
| Event Date | 2026-09-21 |
| Event Location Timezone | America/Los_Angeles |
| Event Start Time | 12:00 PM |
| Event End Time | 4:00 PM |
| Capacity | 10 |
| Registered | 0 |
| Available Place | 10 |
| Created By | Amardeep Grewal |
| Event Date | 2026-09-22 |
| Event Location Timezone | UTC |
| Event Start Time | 10:00 AM |
| Event End Time | 2:00 PM |
| Capacity | Unlimited |
| Registered | 0 |
| Created By | Oleksandr Mamenko |
| Location | Virtual |
CDW Austin Overdrive - HMF
The Hybrid Mesh Firewall: Project Meteor workshop is designed to equip participants with the knowledge and hands-on experience needed to modernize firewall strategies using Cisco’s Hybrid Mesh Firewall technology. This innovative solution unifies security across data centers, cloud, campus, and IoT environments, providing a highly distributed security fabric.
During this session, you will step into the shoes of a fictional engineer at PseudoCo and work through real-world scenarios that highlight the power and flexibility of Cisco’s security solutions.
The workshop will make extensive use of Cisco Security Cloud Control and cover topics such as deployment, SD-WAN configuration, shared objects management, and application segmentation. This is a great opportunity to build hands-on experience and deepen your understanding of modern network security practices through a self-paced workshop.
Key Takeaways
- Clear understanding of Cisco’s Hybrid Mesh Firewall solution and its advantages
- Gain hands-on experience with Cisco Security Cloud Control for centralized and extensive security management
- Understand how to configure SD-WAN for optimized and secure network connectivity
- Explore enhanced cloud visibility to monitor and protect distributed applications and data
- Deepen your knowledge of Shared Objects and their role in efficient policy management
- Master application segmentation techniques using both endpoint agents and the firewall for comprehensive security.
Who Should Attend
- Anyone involved in firewall management, policy enforcement, or security modernization initiatives
Workshop Format
- Duration: 2 hours
- Structure: A multi-phase, self-contained hands-on workshop
- Phases Include:
- Onboarding firewalls and simplifying branch connectivity
- Integrating cloud policies and multi-cloud defense
- Configuring segmentation for workloads and applications
- Testing threat detection capabilities including encrypted traffic inspection
- Tools Used: Cisco Security Cloud Control, Secure Firewall, Multi-cloud Defense and Secure Workload
SHAPE
Prerequisites
- Cisco account registration (CCOID) – Click here for more information
- Cisco Security Workshop account registration – Click here to register
- Basic understanding of firewall concepts and network security
SHAPE
Why Attend This Workshop
In today’s complex and rapidly evolving threat landscape, traditional firewall approaches are no longer sufficient. The Hybrid Mesh Firewall: Project Meteor workshop empowers you to modernize your security posture by adopting a distributed firewall fabric that scales with your enterprise needs. Attendees will gain practical skills to reduce attack surfaces, prevent lateral movement, and protect critical applications across hybrid environments. This workshop offers a unique opportunity to experience Cisco’s cutting-edge firewall technology firsthand, enabling you to lead your organization’s security transformation with confidence and agility.
| Event Date | 2026-09-22 |
| Event Location Timezone | America/Chicago |
| Event Start Time | 5:00 AM |
| Event End Time | 11:00 PM |
| Capacity | 25 |
| Registered | 1 |
| Available Place | 24 |
| Created By | Ali Bigdeli |
| Location | Virtual |
CDW Austin Overdrive - AI Defense
Step into the role of a Senior Security Engineer at PseudoCo and take on a mission to secure AI sprawl across the enterprise. Across four real-world use cases and fifteen success criteria. You will:
- Discover AI assets
- Validate models with algorithmic red teaming
- Scan model files for embedded threats
- Build runtime policies that block security threats, sensitive data, and harmful language in real time.
Then you'll go deeper into agentic AI by inspecting flows for agent-specific attacks such as tool poisoning, prompt injection, and rug pull attacks.
| Event Date | 2026-09-22 |
| Event Location Timezone | America/Chicago |
| Event Start Time | 5:00 AM |
| Event End Time | 11:00 PM |
| Capacity | 25 |
| Registered | 0 |
| Available Place | 25 |
| Created By | Eddie Mendonca |
| Location | Cisco Office - Austin |
| Event Date | 2026-09-22 |
| Event Location Timezone | America/New_York |
| Event Start Time | 9:00 AM |
| Event End Time | 8:00 PM |
| Capacity | 20 |
| Registered | 1 |
| Available Place | 19 |
| Created By | Chantel Strickland |
| Location | Cisco ATL |
Norfolk Southern Secure Access Advanced Lab
Congratulations on your new role as lead Security Architect at Securely Sprockets! As the lead, you have wisely chosen Cisco Secure Access as the Zero Trust Platform for Securely Sprockets. Today you will be configuring Secure Access and helping your first user enroll and use resources protected by Cisco Secure Access.

| Event Date | 2026-09-22 |
| Event Location Timezone | America/New_York |
| Event Start Time | 9:00 AM |
| Event End Time | 6:00 PM |
| Capacity | 20 |
| Registered | 0 |
| Available Place | 20 |
| Created By | Oscar Ramirez |
| Location | Virtual |
DC Segmentation w/ Cisco Secure Workload - Sept2026
Workshop Objectives
Throughout this session, you will navigate through six key scenarios designed to showcase the full lifecycle of workload protection:
- UI Navigation & Visibility: Explore the Security Cloud Control portal and understand how software agents provide deep telemetry, including CPU monitoring, process snapshots, and vulnerability identification.
- AI-Driven Policy Discovery: Learn how to use unsupervised machine learning (ADM) to automatically discover application behaviors and suggest relevant security policies.
- Policy Analysis: Understand how to visualize micro-segmentation and use "List" and "Graph" views to interpret complex connection rules.
- Zero-Trust Enforcement: Test policies against live traffic to identify "escaped" flows and move from visibility to active enforcement.
- Agentless Cloud Segmentation: Discover how to extend security to public cloud environments like AWS and EKS without deploying agents, using native cloud controls.
- Advanced Forensics & Security Dashboards: Utilize the Security Dashboard to monitor vulnerability scores, network anomalies, and MITRE ATT&CK-aligned forensic events to identify and stop "bad actors" in real-time.
| Event Date | 2026-09-22 |
| Event Location Timezone | America/Chicago |
| Event Start Time | 9:00 AM |
| Event End Time | 3:00 PM |
| Capacity | 15 |
| Registered | 4 |
| Available Place | 11 |
| Created By | Aaron McDaniel |
| Location | The Root - Downtown Tulsa |
| Event Date | 2026-09-22 |
| Event Location Timezone | America/Chicago |
| Event Start Time | 10:00 AM |
| Event End Time | 5:00 PM |
| Capacity | 15 |
| Registered | 0 |
| Available Place | 15 |
| Created By | Daniel Matthews |
| Location | Virtual |
Jason - Hybrid Mesh Firewall : PseudoCo Project Meteor
The Hybrid Mesh Firewall: Project Meteor workshop is designed to equip participants with the knowledge and hands-on experience needed to modernize firewall strategies using Cisco’s Hybrid Mesh Firewall technology. This innovative solution unifies security across data centers, cloud, campus, and IoT environments, providing a highly distributed security fabric.
During this session, you will step into the shoes of a fictional engineer at PseudoCo and work through real-world scenarios that highlight the power and flexibility of Cisco’s security solutions.
The workshop will make extensive use of Cisco Security Cloud Control and cover topics such as deployment, SD-WAN configuration, shared objects management, and application segmentation. This is a great opportunity to build hands-on experience and deepen your understanding of modern network security practices through a self-paced workshop.
Key Takeaways
- Clear understanding of Cisco’s Hybrid Mesh Firewall solution and its advantages
- Gain hands-on experience with Cisco Security Cloud Control for centralized and extensive security management
- Understand how to configure SD-WAN for optimized and secure network connectivity
- Explore enhanced cloud visibility to monitor and protect distributed applications and data
- Deepen your knowledge of Shared Objects and their role in efficient policy management
- Master application segmentation techniques using both endpoint agents and the firewall for comprehensive security.
Who Should Attend
- Anyone involved in firewall management, policy enforcement, or security modernization initiatives
Workshop Format
- Duration: 2 hours
- Structure: A multi-phase, self-contained hands-on workshop
- Phases Include:
- Onboarding firewalls and simplifying branch connectivity
- Integrating cloud policies and multi-cloud defense
- Configuring segmentation for workloads and applications
- Testing threat detection capabilities including encrypted traffic inspection
- Tools Used: Cisco Security Cloud Control, Secure Firewall, Multi-cloud Defense and Secure Workload
SHAPE
Prerequisites
- Cisco account registration (CCOID) – Click here for more information
- Cisco Security Workshop account registration – Click here to register
- Basic understanding of firewall concepts and network security
SHAPE
Why Attend This Workshop
In today’s complex and rapidly evolving threat landscape, traditional firewall approaches are no longer sufficient. The Hybrid Mesh Firewall: Project Meteor workshop empowers you to modernize your security posture by adopting a distributed firewall fabric that scales with your enterprise needs. Attendees will gain practical skills to reduce attack surfaces, prevent lateral movement, and protect critical applications across hybrid environments. This workshop offers a unique opportunity to experience Cisco’s cutting-edge firewall technology firsthand, enabling you to lead your organization’s security transformation with confidence and agility.
| Event Date | 2026-09-23 |
| Event Location Timezone | Asia/Singapore |
| Event Start Time | 10:00 AM |
| Event End Time | 6:00 PM |
| Capacity | 10 |
| Registered | 3 |
| Available Place | 7 |
| Created By | Foo Hao Chan |
CSW Monthly Test Drive.
The 3-hour Cisco Secure Workload hands-on "Test Drive" provides practical experience using Cisco Secure Workload 4.0 to protect applications, minimise attack surfaces, and automate Zero Trust micro-segmentation.
What to Expect
You will work through the workshop as a Senior Security Engineer at PseudoCo, a fictional organization who are looking to deliver Zero Trust Segmentation.
The workshop includes:
- Mastering the interface, managing software agents, and monitoring real-time resource statistics.
- Leveraging machine learning to automatically map application dependencies and generate Zero Trust policies.
- Exploring policy structures, analysing service conversations, and visualising your security graph.
- Testing policies against live traffic to prevent potential impact, then activating full enforcement.
- Extending your security fabric into AWS using native cloud controls without the need for agents.
- Using vulnerability scores and MITRE ATT&CK techniques to detect and respond to behavioural anomalies.
- Learning how to orchestrate security across your ACI fabric for a unified, hybrid-mesh defence.
Who should Attend
- Security engineers and architects
- Technical Decision Makers
- IT Professionals responsible for application security, micro-segmentation and workload protection
What you will learn
- Get a first-hand look at how to stop lateral movement
- Learn how to identify vulnerable software
- Achieve continuous compliance in complex hybrid environments.
Ready to secure your infrastructure? Join us for this interactive session.
Prerequisites:
Prior to the session, please go to https://id.cisco.com/signin/register for a CCO account. This will be needed to access the workshop and labs.
| Event Date | 2026-09-23 |
| Event Location Timezone | America/New_York |
| Event Start Time | 1:00 PM |
| Event End Time | 3:00 PM |
| Capacity | 30 |
| Registered | 8 |
| Available Place | 22 |
| Created By | Leonardo Milher |
| Location | Virtual |
Cisco ISE - Hands on Workshop for Partners
Master the deployment and configuration of Cisco Identity Services Engine (ISE) through this intensive, hands-on lab. Designed for Field Engineers, this workshop moves you from theory to production-readiness by simulating a real-world deployment for "Stark Industries" within a Cisco dCloud environment.
Learning Objectives
- Deploy: Build a distributed ISE architecture from the ground up.
- Secure: Implement robust authentication, profiling, and guest access policies.
- Manage: Gain proficiency in device administration, patching, and lifecycle management.
- Confidence: Build the technical expertise required to position and deploy ISE in production customer environments.
Lab Agenda:
-
Core Connectivity & Access
- Initial Setup & Distributed Deployment
- Active Directory Integration
- Wired MAB & Device Profiling
- Secure Access (PEAP-MSCHAPv2 & EAP-TLS)
- Sponsored Guest Access
-
Advanced Security & Administration
- BYOD & Remote Access VPN
- Posture Assessment & Remediation
- Device Administration (RADIUS & TACACS+)
- ISE Management (Control, Patching, & Backups)
Logistics
- Format: Hands-on lab scenarios via Cisco dCloud.
- Please bring your own laptop which could connect to Cisco Guest Wifi , then login to https://workshops.cisco.com/ for online lab guide, https://dcloud.cisco.com/ for lab access
| Event Date | 2026-09-24 |
| Event Location Timezone | Australia/Sydney |
| Event Start Time | 9:30 AM |
| Event End Time | 4:30 PM |
| Capacity | 15 |
| Registered | 14 |
| Available Place | 1 |
| Created By | Paul Qiu |
| Location | Cisco Canberra |
| Event Date | 2026-09-24 |
| Event Location Timezone | America/Toronto |
| Event Start Time | 8:00 AM |
| Event End Time | 10:55 AM |
| Capacity | 20 |
| Registered | 0 |
| Available Place | 20 |
| Created By | Charles Kim |
| Location | Cisco Office - Toronto |
One Cisco Experience Lab - Tupelo
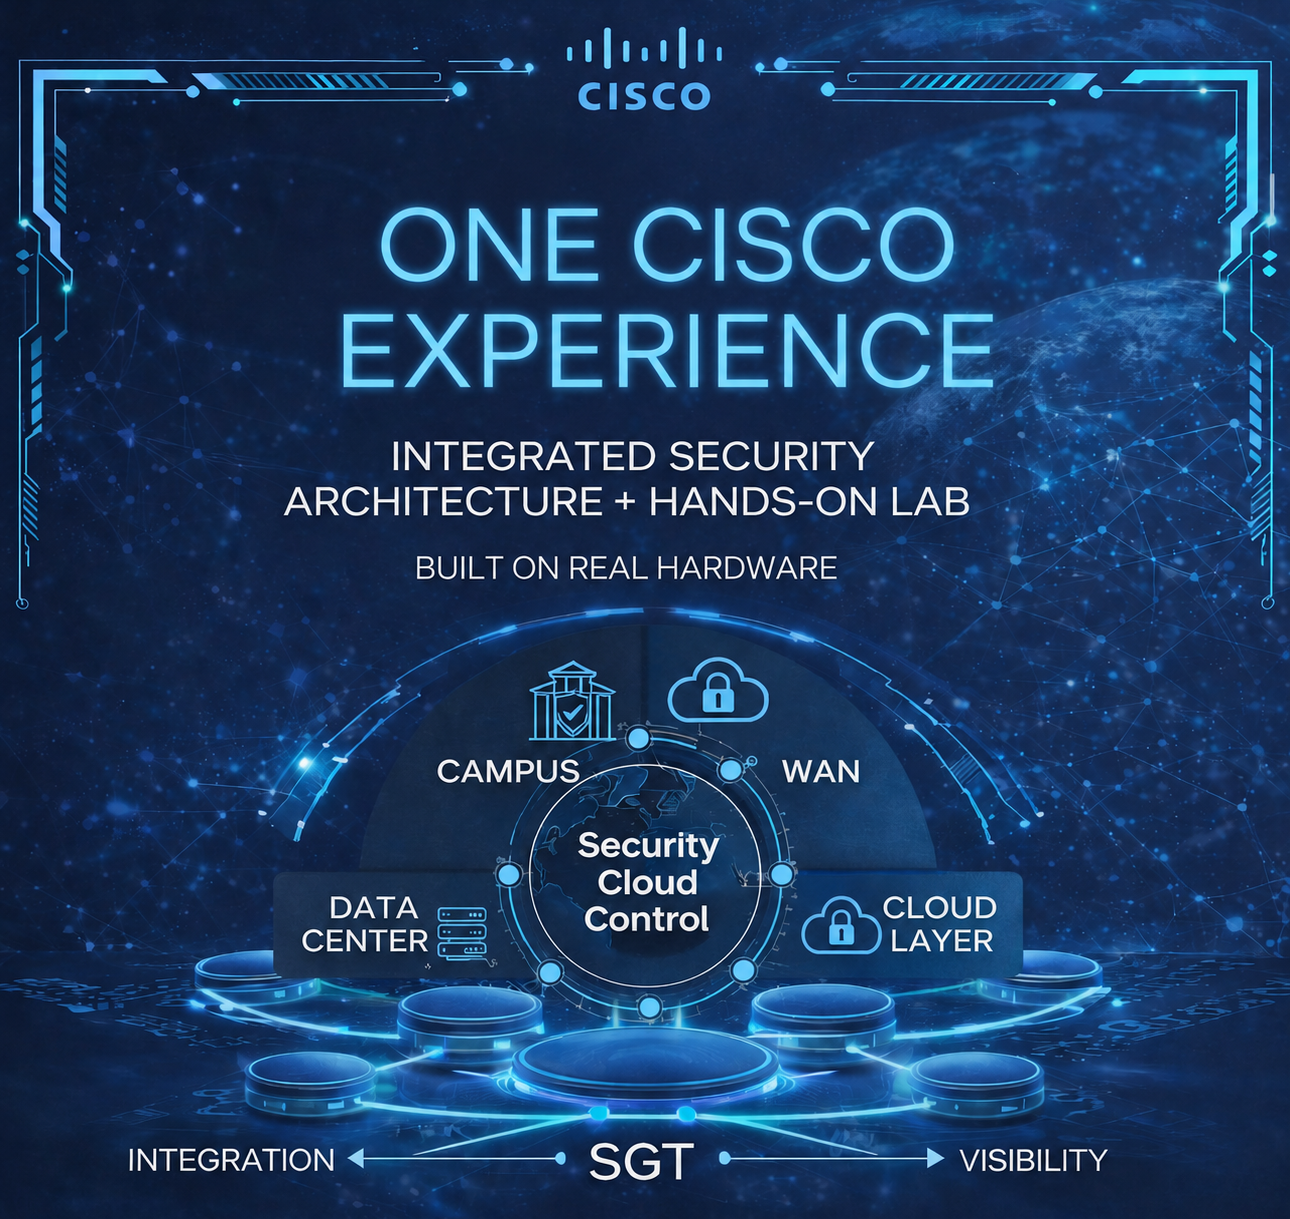
Course Title: One Cisco Experience Lab
Direct Workshop Link: https://ciscosecurityworkshop.com/workshops/mod/page/view.php?id=8229
Course Description:
Get hands-on with the One Cisco Experience by unifying networking, security, observability, and policy into a single integrated architecture designed to protect modern enterprises across campus, branch, WAN, cloud, and remote access environments. By combining deep visibility, identity-driven access control, and Zero Trust enforcement across every connection point, organizations can simplify operations, strengthen security posture, and improve digital resilience.
In this hands-on lab, participants will deploy either a BGP EVPN fabric or an SDA-LISP Campus fabric as the foundation for a modern Cisco Network supporting both macro and micro segmentation. Through guided exercises, you’ll experience how Cisco technologies work together seamlessly across domains using Cisco Security Cloud Control, Secure Firewall Management Center (cdFMC/FTD), Cisco Secure Access, Duo, Catalyst SD-WAN, Identity Services Engine (ISE), ThousandEyes, and Security Group Tags (SGTs) to deliver unified policy enforcement, shared telemetry, and consistent user experiences.
You’ll implement integrated workflows that connect networking and security operations across campus, branch, data center, and remote users. Real-world use cases include securing users and devices accessing local and cloud applications, protecting IoT environments through identity-based segmentation, and enabling secure remote access using Zero Trust Access (ZTA). Participants will also explore how Cisco’s unified platform approach enables consistent policy, end-to-end visibility, and faster troubleshooting across switching, wireless, SD-WAN, cloud security, and firewall infrastructure.
By the end of the lab, you’ll gain practical experience deploying and validating a fully integrated Cisco architecture that demonstrates the power of the One Cisco Experience—bringing together connectivity, security, and observability into a cohesive operational model for the modern enterprise.
Workshop Highlights
- Build a Modern Cisco Network: Deploy either a Cisco SDA-LISP Campus Fabric or BGP EVPN Fabric as the foundation for Zero Trust segmentation and secure connectivity.
- Hands-On Zero Trust Implementation: Configure identity-based access control, SGT-driven segmentation, Secure Access, Duo MFA, and Secure Firewall policy enforcement across campus, WAN, and remote access environments.
- End-to-End Security Integration: Integrate Cisco Security Cloud Control, ISE, Secure Access, SD-WAN, ThousandEyes, and Secure Firewall for unified policy and telemetry sharing.
- Real-World Security Use Cases: Secure users, IoT devices, branch connectivity, SaaS applications, and private applications using practical enterprise scenarios.
- Guided Expert-Led Labs: Follow step-by-step exercises with instructor and proctor support while validating policy enforcement, segmentation, and observability across the infrastructure.
Key Takeaways
- Practical experience deploying a Zero Trust-based Cisco Network architecture.
- Hands-on skills configuring macro and micro segmentation using Virtual Networks (VNs), TrustSec, and Security Group Tags (SGTs).
- Experience integrating Cisco ISE, Duo, Active Directory, Secure Access, SD-WAN, and Secure Firewall into a unified policy framework.
- Understanding of secure remote access technologies including ZTNA, VPN-as-a-Service, and browser-based access.
- Skills to deploy and validate secure campus and branch architectures using Cisco Catalyst Center, SDA, EVPN, and SD-WAN.
- Experience using ThousandEyes and telemetry tools for visibility, monitoring, and troubleshooting.
- Confidence troubleshooting identity, policy, segmentation, and connectivity issues across enterprise environments.
Who Should Attend
- Network engineers and architects designing modern enterprise campus, branch, and WAN infrastructures.
- Security engineers implementing Zero Trust, segmentation, and secure access solutions.
- IT professionals responsible for campus networking, SD-WAN, wireless, or data center security.
- Cisco partners, consultants, and technical teams supporting modern Networking deployments.
- Anyone interested in gaining hands-on experience with Cisco’s integrated Zero Trust and modern Networking architecture.
Workshop Format
- Hands-On Lab: Interactive guided exercises in a fully integrated Hardware Based lab environment.
- Real-World Enterprise Scenarios: Deploy and validate policies across campus, WAN, remote access, IoT, and data center environments.
- Step-by-Step Guided Labs: Instructor-led walkthroughs with hands-on implementation and validation tasks.
- Dedicated Hardware POD Access: Access to a dedicated hardware pod lab environment for independent configuration and testing.
- Expert Support: Live assistance from experienced Cisco Proctors throughout the workshop.
Prerequisites
- Familiarity with basic networking concepts including routing, switching, and wireless networking.
- Basic understanding of security concepts such as VPNs, segmentation, identity, and access control.
- Prior exposure to Cisco networking or security technologies is helpful but not required.
- General knowledge of enterprise networking environments, SD-WAN, or campus architectures is recommended.
- Access to a Cisco dCloud account (provided as part of the course)
Why Attend?
This workshop provides a unique opportunity to gain practical, hands-on experience building and securing a modern enterprise network using Cisco’s Zero Trust architecture. Rather than only learning the concepts, you’ll deploy, integrate, validate, and troubleshoot real security and networking technologies across campus, branch, WAN, cloud, and remote access environments. By the end of the lab, you’ll have the knowledge and confidence to implement unified policy enforcement, secure segmentation, observability, and secure access strategies that help organizations reduce risk and strengthen digital resilience.
| Event Date | 2026-09-24 |
| Event Location Timezone | America/Chicago |
| Event Start Time | 8:30 AM |
| Event End Time | 5:00 PM |
| Capacity | 10 |
| Registered | 6 |
| Available Place | 4 |
| Created By | Jeremy Moore |
Colorado Springs Cisco Secure Access: End User Experience Workshop

Cisco Secure Access is a converged cloud Security Service Edge (SSE) solution that is better for users, easier for IT, and safer for everyone. It enforces modern cybersecurity while providing a seamless and frictionless experience as users connect from anything to anywhere, via a common access approach.
Cisco Secure Access simplifies IT and InfoSec operations through a single, cloud-managed console, unified client, centralized policy creation, and aggregated reporting. Cisco Secure Access extensive security capabilities include:
Clientless Zero Trust Network Access (ZTNA)
Client Zero Trust Network Access (ZTNA)
VPN as a Service (VPNaaS)
Digital Experience Monitoring (DEM)
Firewall as a Service (FWaaS)
Intrusion Prevention System (IPS)
Domain Name System (DNS) Security
Secure Web Gateway (SWG)
Multimode Malware Protection
Cloud Access Security Broker (CASB)
Data Loss Prevention (DLP)
Remote Browser Isolation (RBI)
The emphasis on this lab is walking through a number of scenarios to experience what an end user would in an environment with Cisco Secure Access implemented. Note, there is only read-only access in the Secure Access console.
Key Takeaways
- Gain firsthand experience with Cisco Secure Access features and capabilities, such as Zero Trust Network Access (ZTNA), Secure Web Gateway (SWG), and Firewall as a Service (FWaaS).
- Understand how Cisco Secure Access delivers a seamless and secure user experience while simplifying IT and InfoSec operations.
- Learn how to navigate a unified, cloud-managed console for centralized policy creation, aggregated reporting, and a unified client experience.
- See how advanced security features like Data Loss Prevention (DLP), Cloud Access Security Broker (CASB), and Remote Browser Isolation (RBI) can protect your organization’s critical assets.
- Discover how to assess digital experience performance with integrated Digital Experience Monitoring (DEM).
What to Expect
- A hands-on walkthrough of real-world scenarios to experience how Cisco Secure Access operates from an end-user perspective.
- An introduction to the Secure Access console (read-only access) to explore its functionalities and understand its role in simplifying IT operations.
- Insights into how Cisco Secure Access integrates with your existing IT infrastructure to enforce modern cybersecurity practices.
- Practical demonstrations of the platform’s capabilities, including Zero Trust principles, advanced malware protection, and secure access management.
Who Should Attend
- IT Security Professionals: Looking to enhance their organization’s security posture with a unified Security Service Edge (SSE) solution.
- IT Administrators: Interested in simplifying operations through centralized policy management and a cloud-managed console.
- CISOs and Security Leaders: Evaluating modern security solutions to meet the demands of hybrid work environments.
- Network Engineers: Seeking to understand how Cisco Secure Access integrates with existing network architectures.
- Compliance Officers: Focused on data loss prevention, policy enforcement, and regulatory compliance.
Workshop Format
- Duration: 2-3 hours (flexible based on the audience needs).
- Interactive Scenarios: Participants will walk through guided scenarios to experience Cisco Secure Access in action.
- Hands-On Exploration: Engage with the Secure Access console (read-only) to understand the platform’s interface and key functionalities.
- Q&A Session: Time allocated for participants to ask technical questions and receive expert guidance.
- Virtual or In-Person: The lab can be conducted in a virtual or on-site format, depending on your organization’s preference.
Why Attend
- Future-Proof Your Security Strategy: Learn how Cisco Secure Access addresses modern security challenges, including securing hybrid work environments and protecting against sophisticated threats.
- Simplify IT Operations: See how a unified console and centralized policy creation can reduce complexity and improve efficiency for your IT team.
- Enhance User Experience: Discover how Cisco Secure Access provides a seamless and frictionless experience for end users, enabling productivity without compromising security.
- Real-World Scenarios: Gain practical insights into how Secure Access operates in real-world scenarios, giving you the confidence to implement and manage the solution.
- Expert Insights: Get guidance from Cisco experts who will walk you through the platform’s features and answer your specific questions.
This workshop is an excellent opportunity to experience the power and simplicity of Cisco Secure Access firsthand and understand how it can help your organization enforce modern cybersecurity while enhancing productivity and efficiency. Sign up now to secure your spot!
| Event Date | 2026-09-24 |
| Event Location Timezone | America/Denver |
| Event Start Time | 9:00 AM |
| Event End Time | 1:00 PM |
| Capacity | 45 |
| Registered | 6 |
| Available Place | 39 |
| Created By | jefdoole@cisco.com |
| Location | Trace3 Office |
Colorado Springs Cisco Secure Access: End User Experience Workshop (2)
Cisco Secure Access is a converged cloud Security Service Edge (SSE) solution that is better for users, easier for IT, and safer for everyone. It enforces modern cybersecurity while providing a seamless and frictionless experience as users connect from anything to anywhere, via a common access approach.
Cisco Secure Access simplifies IT and InfoSec operations through a single, cloud-managed console, unified client, centralized policy creation, and aggregated reporting. Cisco Secure Access extensive security capabilities include:
Clientless Zero Trust Network Access (ZTNA)
Client Zero Trust Network Access (ZTNA)
VPN as a Service (VPNaaS)
Digital Experience Monitoring (DEM)
Firewall as a Service (FWaaS)
Intrusion Prevention System (IPS)
Domain Name System (DNS) Security
Secure Web Gateway (SWG)
Multimode Malware Protection
Cloud Access Security Broker (CASB)
Data Loss Prevention (DLP)
Remote Browser Isolation (RBI)
The emphasis on this lab is walking through a number of scenarios to experience what an end user would in an environment with Cisco Secure Access implemented. Note, there is only read-only access in the Secure Access console.
Key Takeaways
- Gain firsthand experience with Cisco Secure Access features and capabilities, such as Zero Trust Network Access (ZTNA), Secure Web Gateway (SWG), and Firewall as a Service (FWaaS).
- Understand how Cisco Secure Access delivers a seamless and secure user experience while simplifying IT and InfoSec operations.
- Learn how to navigate a unified, cloud-managed console for centralized policy creation, aggregated reporting, and a unified client experience.
- See how advanced security features like Data Loss Prevention (DLP), Cloud Access Security Broker (CASB), and Remote Browser Isolation (RBI) can protect your organization’s critical assets.
- Discover how to assess digital experience performance with integrated Digital Experience Monitoring (DEM).
What to Expect
- A hands-on walkthrough of real-world scenarios to experience how Cisco Secure Access operates from an end-user perspective.
- An introduction to the Secure Access console (read-only access) to explore its functionalities and understand its role in simplifying IT operations.
- Insights into how Cisco Secure Access integrates with your existing IT infrastructure to enforce modern cybersecurity practices.
- Practical demonstrations of the platform’s capabilities, including Zero Trust principles, advanced malware protection, and secure access management.
Who Should Attend
- IT Security Professionals: Looking to enhance their organization’s security posture with a unified Security Service Edge (SSE) solution.
- IT Administrators: Interested in simplifying operations through centralized policy management and a cloud-managed console.
- CISOs and Security Leaders: Evaluating modern security solutions to meet the demands of hybrid work environments.
- Network Engineers: Seeking to understand how Cisco Secure Access integrates with existing network architectures.
- Compliance Officers: Focused on data loss prevention, policy enforcement, and regulatory compliance.
Workshop Format
- Duration: 2-3 hours (flexible based on the audience needs).
- Interactive Scenarios: Participants will walk through guided scenarios to experience Cisco Secure Access in action.
- Hands-On Exploration: Engage with the Secure Access console (read-only) to understand the platform’s interface and key functionalities.
- Q&A Session: Time allocated for participants to ask technical questions and receive expert guidance.
- Virtual or In-Person: The lab can be conducted in a virtual or on-site format, depending on your organization’s preference.
Why Attend
- Future-Proof Your Security Strategy: Learn how Cisco Secure Access addresses modern security challenges, including securing hybrid work environments and protecting against sophisticated threats.
- Simplify IT Operations: See how a unified console and centralized policy creation can reduce complexity and improve efficiency for your IT team.
- Enhance User Experience: Discover how Cisco Secure Access provides a seamless and frictionless experience for end users, enabling productivity without compromising security.
- Real-World Scenarios: Gain practical insights into how Secure Access operates in real-world scenarios, giving you the confidence to implement and manage the solution.
- Expert Insights: Get guidance from Cisco experts who will walk you through the platform’s features and answer your specific questions.
This workshop is an excellent opportunity to experience the power and simplicity of Cisco Secure Access firsthand and understand how it can help your organization enforce modern cybersecurity while enhancing productivity and efficiency. Sign up now to secure your spot!
| Event Date | 2026-09-24 |
| Event Location Timezone | America/Denver |
| Event Start Time | 9:00 AM |
| Event End Time | 1:00 PM |
| Capacity | 45 |
| Registered | 0 |
| Available Place | 45 |
| Created By | jefdoole@cisco.com |
| Location | Trace3 Office |
| Event Date | 2026-09-24 |
| Event Location Timezone | America/Toronto |
| Event Start Time | 11:00 AM |
| Event End Time | 1:55 PM |
| Capacity | 20 |
| Registered | 0 |
| Available Place | 20 |
| Created By | Charles Kim |
| Location | Cisco Office - Toronto |
| Event Date | 2026-09-24 |
| Event Location Timezone | America/Toronto |
| Event Start Time | 2:00 PM |
| Event End Time | 4:55 PM |
| Capacity | 20 |
| Registered | 0 |
| Available Place | 20 |
| Created By | Charles Kim |
| Location | Cisco Office - Toronto |
CR&R Secure Internet Access
Course Title:
Designing and Deploying Zero Trust Access with Duo Identity and Cisco Secure Access
Course Description:
Step into the role of a network security administrator in this guided, hands-on workshop. You’ll learn how to design, deploy, and validate a modern Zero Trust Access solution using Duo Directory and Cisco Secure Access. Acting as the administrator for the fictional organization PseudoCo, you will configure secure connectivity between remote users and private applications hosted in a secure data center.
You’ll have full administrative access to a dedicated virtual data center environment in Cisco’s dCloud, pre-provisioned with Duo and Secure Access services. Each participant receives a unique Duo tenant and Secure Access organization, enabling you to configure and test infrastructure in any Duo region or Secure Access region, with recommendations to align settings with your specific dCloud Data Center location.
Workshop Highlights
- Real-World Zero Trust Scenarios: Configure secure connectivity for remote users, private applications, and secure Internet access
- Hands-On Labs: Access to a fully provisioned virtual data center and unique Secure Access organization.
- End-to-End Deployment: Learn to set up secure Identity, VPNs, IP pools, and tunnels for seamless, secure access.
- Expert Guidance: Step-by-step lab exercises and access to proctors for support.
Key Takeaways
- Practical experience deploying Zero Trust Access solutions using Duo Identity and Cisco Secure Access.
- Skills to configure and validate secure connections between distributed users and applications.
- Understanding of best practices for aligning Secure Access configurations with data center regions.
Who Should Attend
- IT and network administrators responsible for securing enterprise access.
- Security engineers and architects interested in Zero Trust methodologies.
- Anyone preparing to deploy Duo or Cisco Secure Access solutions in their organization.
Workshop Format
- Hands-On Labs: Interactive, guided exercises in a live dCloud virtual environment.
- Instructor Support: Direct assistance from proctors and subject matter experts.
- Individual Access: Each attendee receives their own Duo account and Secure Access organization and isolated lab environment.
Prerequisites
- Familiarity with basic networking and security concepts.
- Prior experience with remote access technologies or Cisco solutions is helpful but not required.
- Access to a Cisco dCloud account (provided as part of the course).
Why Attend?
This workshop offers a unique, practical opportunity to master Zero Trust Access with Duo Identity and Cisco Secure Access in a risk-free, fully supported lab environment. You’ll leave with the confidence and know-how to implement secure, modern access solutions tailored to your organization’s needs.
| Event Date | 2026-09-24 |
| Event Location Timezone | America/Los_Angeles |
| Event Start Time | 1:00 PM |
| Event End Time | 7:00 PM |
| Capacity | 10 |
| Registered | 0 |
| Available Place | 10 |
| Created By | Amardeep Grewal |
| Event Date | 2026-09-29 |
| Event Location Timezone | Europe/Berlin |
| Event Start Time | 10:00 AM |
| Event End Time | 6:00 PM |
| Capacity | 30 |
| Registered | 0 |
| Available Place | 30 |
| Created By | Dennis Weber |
| Location | Virtual |